Privacy Notice
What personal data iSmartPay collects, why, who we share it with, how long we keep it, and the rights you have under the Data Protection Act, 2012 (Act 843).
iSG-LEG-00002 · Version 1.00 · 12 August 2026
The short version
This summary is for convenience. The detail is in the sections that follow and, where they differ, the detail applies.
- Why do you have my data?Mostly because we need it to move your money and because the law requires us to know who our customers are.
- Do you sell my data?No. We do not sell personal data and we do not share it for anyone else’s marketing.
- Who sees it?Our staff who need it, the banks and operators that move the money, our technology and verification providers, and regulators and law enforcement where the law requires.
- Does it leave Ghana?Some of it, to cloud and service providers. Section 8 explains the protections that apply.
- How long do you keep it?Usually seven years after our relationship ends, because our licence and the anti-money laundering law require it. Section 9 has the detail.
- Can I ask you to delete it?You can ask. We often cannot, because keeping it is a legal requirement. We will always tell you why.
- Can I opt out of marketing?Yes, at any time, and it costs you nothing. It will not affect the service you receive.
- Can I complain?Yes — to our Data Protection Officer first, and then to the Data Protection Commission if you are not satisfied.
What we do not do with your data.
- We do not sell your personal data. Not to advertisers, not to data brokers, not to anyone.
- We do not share your data so that another organisation can market to you.
- We do not use your transaction data to build profiles for advertising.
- We do not give a merchant more data about a payer than it needs to complete the transaction and deal with a dispute.
Your rights.
Act 843 gives you these rights. Exercising them is free, and you do not need to give a reason.
- Be informedTo know how we use your data — which is what this notice is for
- AccessTo ask for a copy of the personal data we hold about you and information about how we use itLimits: We may withhold material where disclosure would breach the prohibition in section 5.2, reveal another person’s data, or prejudice an investigation
- CorrectionTo have inaccurate data corrected and incomplete data completedLimits: We may need evidence of the correct position, particularly for verified identity data
- DeletionTo ask us to delete your dataLimits: Usually we cannot. Our licence and Act 1044 require us to retain records. We will always tell you which obligation prevents deletion
- ObjectTo object to processing based on our legitimate interest, and to marketingLimits: We must stop marketing immediately. For other processing we may continue only if we have compelling grounds that override your objection
- RestrictTo ask us to pause processing while a dispute about accuracy or lawfulness is resolvedLimits: We may still store the data and use it for legal claims
- Withdraw consentTo withdraw consent for anything we do on that basisLimits: Withdrawal is not retrospective; it does not affect what we did lawfully before
- Not be subject to a decision made only by a machineTo ask for human review of an automated decision that affects youLimits: Section 3.3 explains the position and the one situation where we cannot explain
- ComplainTo complain to us and to the Data Protection Commission
How to use a right
- 1. Contact usEmail dpo@ismartpay.com.gh, use the privacy section of the app, or write to the Data Protection Officer at our registered office
- 2. Tell us what you wantSay which right you are exercising and what data it concerns. You do not need to use legal language
- 3. We verify who you areWe will ask you to confirm your identity. This protects you — we will not hand your data to someone claiming to be you
- 4. We acknowledgeWithin 1 Business Day
- 5. We respondWithin the period set by Act 843. We aim to respond sooner and will tell you if a request is complex and needs longer
- 6. If we refuseWe tell you why, which right or obligation prevents us, and how to complain
Questions or complaints.
Come to us first. If you are not satisfied with our response, you can complain to the Data Protection Commission at any time.
- Data Protection Officerdpo@ismartpay.com.gh
- Complaintscomplaints@ismartpay.com.gh
- General contactsupport@ismartpay.com.gh / 0557075426
- Registered officeG-286-2423, Rabat Plot 2 near Gethsemane Cemetery, East Legon, Zaire Street
Where else you can go
- Bank of GhanaComplaints about a payment service, where iSmart Ghana has not resolved the matter within the published timeline or the outcome is disputedBank of Ghana, Market Conduct Office, Accra — after first raising the matter with iSmart Ghana
- Data Protection CommissionComplaints about the handling of personal dataData Protection Commission, Accra — after first raising the matter with the iSmart Ghana Data Protection Officer
- Financial Intelligence CentreNot a complaint route; the body to which iSmart Ghana reports suspicion under Act 1044iSmart Ghana cannot confirm or deny whether any report has been made
- Card schemesDisputes about a card transaction, through the cardholder’s issuing bankCardholders raise card disputes with their own bank, not with iSmart Ghana
Company details
- Legal name
- iSmart International Ghana Limited
- Trading name
- iSmartPay
- Company type
- Company limited by shares, incorporated in Ghana under the Companies Act, 2019 (Act 992)
- Company registration number
- CS681282015
- Tax identification number
- C000524259
- Regulatory status
- Licensed by the Bank of Ghana as a Payment Service Provider under the Payment Systems and Services Act, 2019 (Act 987)
- Licence number
- [To be inserted from the Bank of Ghana licence]
- Data controller registration
- Registered with the Data Protection Commission under the Data Protection Act, 2012 (Act 843) — registration number [to be inserted]
The full Privacy Notice.
Every section of the notice, as approved. Search for a word or open the part you need.
About This Notice
About This Notice
This notice explains what personal data iSmart Ghana collects, why we collect it, what we do with it, who we share it with, how long we keep it, and what rights you have. It is written to be understood by the people it describes, not only by lawyers.
It applies to everyone whose personal data we handle: customers who hold a wallet or use our apps, people who pay merchants through us, merchants and the individuals behind them, people who visit our website, and people who contact us or apply to use our services. Where a section applies to only one group, it says so.
We are required to give you this information by the Data Protection Act, 2012 (Act 843). Nothing in this notice reduces your rights under that Act.
1.1 Who We Are and How to Reach Us
iSmart International Ghana Limited is the data controller for the personal data described in this notice, except where section 4 says we act as a processor on a merchant’s instruction.
| Item | Detail |
|---|---|
| Legal name | iSmart International Ghana Limited |
| Trading name | iSmartPay |
| Company type | Company limited by shares, incorporated in Ghana under the Companies Act, 2019 (Act 992) |
| Company registration number | CS681282015 |
| Tax identification number | C000524259 |
| Registered office | G-286-2423, Rabat Plot 2 near Gethsemane Cemetery, East Legon, Zaire Street |
| Regulatory status | Licensed by the Bank of Ghana as a Payment Service Provider under the Payment Systems and Services Act, 2019 (Act 987) |
| Licence number | [To be inserted from the Bank of Ghana licence] |
| Data controller registration | Registered with the Data Protection Commission under the Data Protection Act, 2012 (Act 843) — registration number [to be inserted] |
| General contact | support@ismartpay.com.gh / 0557075426 |
| Data Protection Officer | dpo@ismartpay.com.gh |
| Complaints | complaints@ismartpay.com.gh |
Our Data Protection Officer is responsible for overseeing how we handle personal data and is your first point of contact for any question or complaint about it. Write to dpo@ismartpay.com.gh, or to the Data Protection Officer at our registered office.
1. Whose Data This Notice Covers
Whose Data This Notice Covers
| Category | Who this is | Our role |
|---|---|---|
| End users | People who hold an iSmartPay wallet or use our apps in a personal capacity | Controller |
| Payers | People who pay a merchant through us without holding an account with us | Controller for our own regulatory and fraud purposes; processor for the merchant otherwise |
| Beneficiaries | People who receive a payout we make on a merchant’s instruction | Controller for our own regulatory purposes |
| Merchant representatives | Directors, beneficial owners, signatories, administrators and staff of merchant businesses | Controller |
| Applicants | People and businesses that apply to use our services, whether or not they are accepted | Controller |
| Website and app visitors | People who visit our website or open our apps | Controller |
| Correspondents | People who contact us with an enquiry, complaint or request | Controller |
| Partner and supplier contacts | Individuals at organisations we work with | Controller |
This notice does not cover our employees and job applicants. Their personal data is covered by a separate internal notice held by Human Resources.
2. What Data We Collect
2.1 Data You Give Us
| Category | Examples |
|---|---|
| Identity | Full name, date of birth, gender, nationality, national identification number, passport or Ghana Card details, photograph or selfie for verification |
| Contact | Mobile number, email address, residential address, business address |
| Business (merchants) | Business name, registration number, tax identification number, ownership and control structure, directors, signatories, business activity, expected volumes, bank account details |
| Financial | Bank account and mobile money details, card details where you pay by card, source of funds and source of wealth information where we are required to ask |
| Relationship | Your correspondence with us, complaints, dispute submissions, call recordings and chat transcripts, marketing preferences |
| Documents | Identity documents, proof of address, certificates of incorporation, business permits, bank statements and any other document we ask for |
2.2 Data We Generate or Observe
| Category | Examples |
|---|---|
| Transaction | Amount, currency, date and time, payment rail, counterparty details, references and narrations, status and status history, fees applied |
| Device and technical | IP address, device identifier, device model and operating system, app version, language, time zone, crash and diagnostic data |
| Usage | Pages and screens viewed, features used, session times, referring website |
| Security and fraud | Login attempts, authentication events, device fingerprints, behavioural signals used to detect fraud, risk scores |
| Account | Account status, verification tier, limits, risk rating, restriction history |
2.3 Data We Obtain From Others
| Source | What we obtain | Why |
|---|---|---|
| National identity and registry services | Confirmation that identity details match an official record | To verify you, as the law requires |
| Registrar of Companies and tax authority | Business registration and tax status | To verify a merchant |
| Sanctions, politically exposed person and adverse media databases | Whether you appear on a list | To meet our obligations under Act 1044 and Act 762 |
| Credit reference and fraud prevention agencies | Identity confirmation and fraud indicators | To verify you and prevent fraud |
| Banks, mobile money operators, GhIPSS, card schemes and acquirers | Transaction and account information | To complete and reconcile transactions |
| Merchants | Data about a payer, where you pay a merchant through us | To complete the transaction and meet our own obligations |
| Publicly available sources | Information relevant to due diligence | To assess risk where the law requires |
2.4 Special Categories and Children
We do not seek data revealing your health, religion, ethnicity, political opinions or trade union membership, and you should not send it to us. Where such data reaches us incidentally — for example in a document you upload or a complaint you write — we hold it only for as long as we need to and do not use it to make decisions about you.
We use biometric data only where you choose to enable fingerprint or face recognition to unlock our app, or where a selfie is used to verify your identity against an identity document. Where biometric unlocking is used, the biometric stays on your device and we never receive it.
Our services are not for people under 18. We do not knowingly collect data about children. If you believe we hold data about a child, contact our Data Protection Officer and we will delete it unless the law requires us to keep it.
3. Why We Use Your Data, and Our Lawful Basis
Why We Use Your Data, and Our Lawful Basis
Act 843 requires us to have a lawful basis for every purpose. The table below states each purpose and the basis we rely on. Where we rely on a legal obligation or on the performance of a contract, you cannot ask us to stop — but you can ask us to explain, and you can challenge whether the basis is right.
| What we use it for | Data used | Our lawful basis |
|---|---|---|
| Opening your account and verifying who you are | Identity, contact, business, documents, data from registries and identity services | Legal obligation under Act 1044 and Act 987; performance of our contract with you |
| Screening you against sanctions, PEP and adverse media lists | Identity, business, ownership | Legal obligation under Act 1044 and Act 762 |
| Processing your transactions | Transaction, financial, identity, device | Performance of our contract with you |
| Monitoring transactions for money laundering and terrorist financing | Transaction, identity, behavioural | Legal obligation under Act 1044 |
| Preventing, detecting and investigating fraud | Transaction, device, security, behavioural, identity | Legal obligation; our legitimate interest in protecting you and us from fraud |
| Reconciling and settling | Transaction, financial | Performance of our contract; legal obligation under Act 987 |
| Handling your complaints and disputes | Relationship, transaction, identity, call recordings | Performance of our contract; legal obligation under Act 987 and BoG guidelines |
| Providing support and communicating with you about your account | Contact, relationship, account | Performance of our contract |
| Managing risk, limits and creditworthiness of a merchant relationship | Business, transaction, financial, risk | Performance of our contract; our legitimate interest in managing our exposure |
| Keeping our services secure and available | Device, technical, usage, security | Our legitimate interest in operating a secure service; legal obligation under BoG cyber directives |
| Meeting our reporting duties to the Bank of Ghana and the Financial Intelligence Centre | Identity, transaction, account | Legal obligation under Act 987 and Act 1044 |
| Keeping records and responding to regulators, auditors and courts | All categories | Legal obligation |
| Improving our services and understanding how they are used | Usage, device, transaction — aggregated or de-identified wherever possible | Our legitimate interest in improving what we offer |
| Marketing our services to you | Contact, relationship, usage | Your consent, which you may withdraw at any time |
| Establishing, exercising or defending legal claims | All categories relevant to the claim | Our legitimate interest in defending our position; legal obligation |
3.1 Where We Rely on Legitimate Interest
Where we rely on legitimate interest, we have weighed our interest against your rights and concluded that our use is proportionate and would not surprise you. You may object to any use based on legitimate interest — section 10 explains how — and we will stop unless we have compelling grounds that override your objection.
3.2 Where We Rely on Consent
We rely on consent only for marketing and for optional features such as non-essential cookies and biometric app unlocking. Consent is genuinely optional: refusing or withdrawing it will not affect the service you receive, and withdrawing it is as easy as giving it. Withdrawal does not affect anything we did lawfully before you withdrew.
3.3 Automated Decisions
We use automated systems to screen transactions for fraud and financial crime, to apply limits, and to assign risk ratings. These systems can cause a transaction to be declined, an account to be restricted, or an application to be referred for review.
A decision to decline or terminate a relationship on financial crime grounds is always reviewed by a person before it takes effect, except where an immediate automated block is necessary to prevent a transaction we are prohibited from processing.
You may ask us to explain a decision, ask for human review, and contest it — except where telling you would breach the prohibition in section 5.2. This is a real limit and we would rather state it than pretend otherwise.
4. When We Act for a Merchant Rather Than for Ourselves
When We Act for a Merchant Rather Than for Ourselves
If you pay a merchant through iSmartPay, two organisations handle your data and they do so in different capacities.
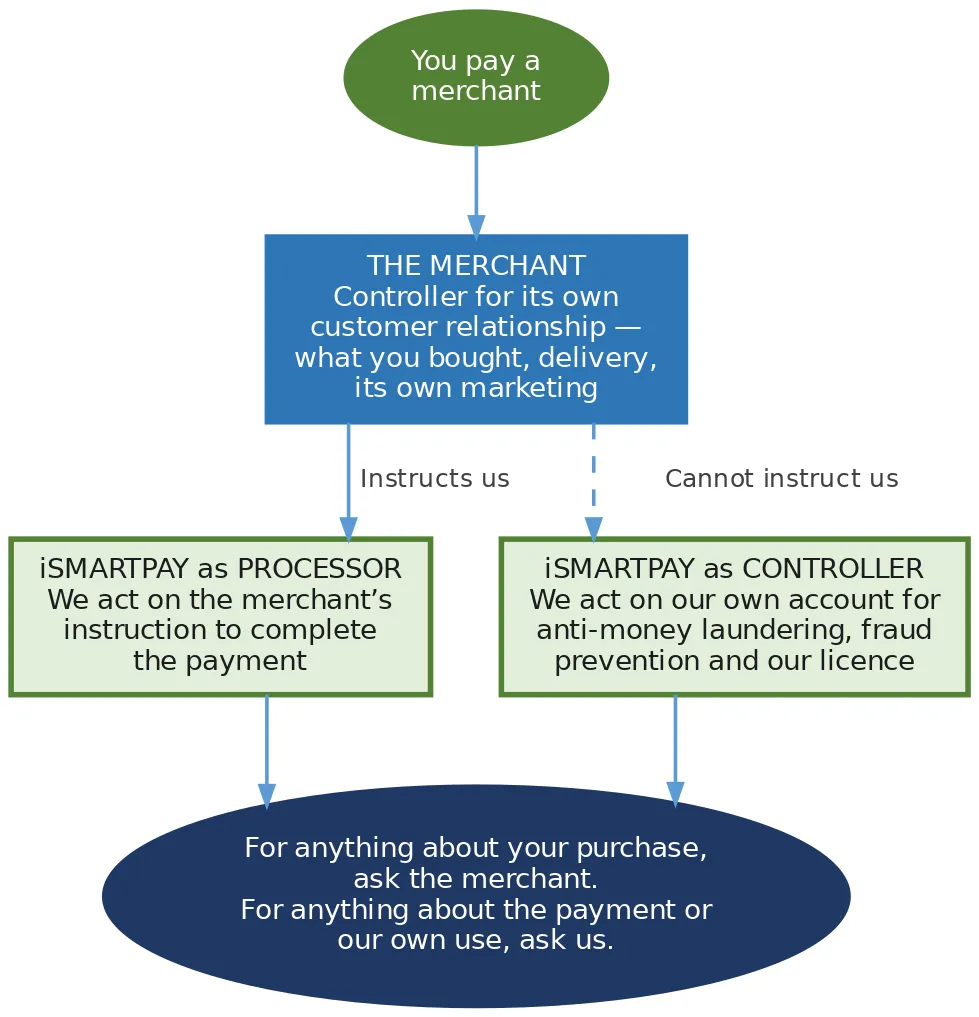
Figure 1 — Who is responsible for what when you pay a merchant. The merchant cannot instruct us on the parts where we act as controller, because those obligations are ours under the law.
As a processor, we act only on the merchant’s instructions, we do not use the data for our own purposes, and questions about your purchase should go to the merchant. Our processing agreement with each merchant requires appropriate security, confidentiality, assistance with your rights, and deletion or return of data at the end.
As a controller, we act on our own account and no merchant can instruct us otherwise. This covers our anti-money laundering duties, sanctions screening, fraud prevention, transaction monitoring, record keeping and reporting to regulators.
Merchants are responsible for their own compliance with Act 843 in relation to their customers, including giving their customers their own privacy notice.
7. How We Protect Your Data
How We Protect Your Data
We hold a Payment Service Provider licence and we operate an information security management system aligned to ISO/IEC 27001:2022. Where we handle card data we do so in accordance with the Payment Card Industry Data Security Standard.
| Measure | What it means in practice |
|---|---|
| Encryption | Your data is encrypted when it travels between you and us, and when it is stored |
| Card data isolation | Card numbers are captured in a segregated secure environment and replaced by a token. Our operational staff never see your full card number, and we never store your CVV or PIN |
| Access on need | Staff have access only to what their role requires; privileged access is time-limited and separately approved; access is reviewed every quarter and removed the day someone leaves |
| Logging | Access to systems holding personal data is logged, and the logs cannot be altered |
| Testing | We test our defences regularly, including an annual penetration test of the payment platform |
| Supplier control | Providers who handle personal data for us are assessed before we engage them and are bound by written data protection terms |
| Training | Everyone who works here is trained on data protection when they join and every year afterwards |
| Breach response | We have a defined process for detecting, containing and reporting a personal data breach |
If a breach affecting your data occurs, we will notify the Data Protection Commission within the statutory period and will tell you without undue delay where the breach is likely to affect your rights, explaining what happened, what data was involved, what we are doing, and what you should do.
No system is perfectly secure. Please help us by keeping your credentials secret and telling us immediately if you think your account has been compromised. We will never ask you for your PIN, password or one-time code.
8. Sending Data Outside Ghana
Sending Data Outside Ghana
Some of our providers, particularly cloud hosting and software providers, process data outside Ghana. Act 843 permits this where appropriate protection is in place.
| Safeguard | What we do |
|---|---|
| Assessment before transfer | We assess the destination and the provider before any personal data is transferred |
| Contractual protection | Every recipient is bound by written terms requiring protection at least equivalent to Act 843, restricting use to our instructions, and requiring assistance with your rights |
| Minimisation | We transfer only what is necessary, and we prefer providers who can host data in or near Ghana |
| Security conditions | Encryption in transit and at rest, access control, and audit rights |
| Ongoing review | Transfers are reviewed annually by our Data Protection Officer |
You may ask our Data Protection Officer where your data is processed and what safeguards apply.
9. How Long We Keep Your Data
How Long We Keep Your Data
We keep personal data only as long as we need it. In our industry that is usually longer than people expect, because our licence and the anti-money laundering law require us to be able to produce records years after a relationship ends.
| What | How long | Why |
|---|---|---|
| Merchant records — due diligence, ownership, contracts | 7 years after the relationship ends | Act 987 and Act 1044 record-keeping obligations |
| End user account and verification records | 5 years after closure, minimum | Act 1044 record-keeping obligation |
| Transaction records | 7 years from the transaction | Act 987; audit and tax requirements |
| Screening, monitoring and alert records | 7 years | Act 1044 |
| Suspicion reports and related material | 5 years minimum, access strictly restricted | Act 1044 |
| Complaints and disputes | 7 years from closure | Act 987 and BoG complaint handling requirements |
| Call recordings and chat transcripts | 2 years, or longer where a dispute is open | Evidence of what was agreed; complaint handling |
| Applications that were declined or abandoned | 5 years | To evidence the decision and to meet Act 1044 obligations |
| Marketing preferences | Until you withdraw consent, plus 2 years | To evidence that we respected your choice |
| Website and app analytics | 26 months, in de-identified form where possible | Our legitimate interest in improving the service |
| Security and access logs | 7 years | Act 987, PCI DSS and ISO/IEC 27001 requirements |
When a retention period ends we delete the data or de-identify it so that it can no longer be linked to you. Where data is held in a backup, deletion takes effect when the backup cycles, and the data is not used in the meantime.
10. Your Rights
Your Rights
Act 843 gives you the rights below. Exercising them is free, and you do not need to give a reason.
| Right | What it means | Limits that may apply |
|---|---|---|
| Be informed | To know how we use your data — which is what this notice is for | None |
| Access | To ask for a copy of the personal data we hold about you and information about how we use it | We may withhold material where disclosure would breach the prohibition in section 5.2, reveal another person’s data, or prejudice an investigation |
| Correction | To have inaccurate data corrected and incomplete data completed | We may need evidence of the correct position, particularly for verified identity data |
| Deletion | To ask us to delete your data | Usually we cannot. Our licence and Act 1044 require us to retain records. We will always tell you which obligation prevents deletion |
| Object | To object to processing based on our legitimate interest, and to marketing | We must stop marketing immediately. For other processing we may continue only if we have compelling grounds that override your objection |
| Restrict | To ask us to pause processing while a dispute about accuracy or lawfulness is resolved | We may still store the data and use it for legal claims |
| Withdraw consent | To withdraw consent for anything we do on that basis | Withdrawal is not retrospective; it does not affect what we did lawfully before |
| Not be subject to a decision made only by a machine | To ask for human review of an automated decision that affects you | Section 3.3 explains the position and the one situation where we cannot explain |
| Complain | To complain to us and to the Data Protection Commission | None |
10.1 How to Exercise a Right
| Step | Detail |
|---|---|
| 1. Contact us | Email dpo@ismartpay.com.gh, use the privacy section of the app, or write to the Data Protection Officer at our registered office |
| 2. Tell us what you want | Say which right you are exercising and what data it concerns. You do not need to use legal language |
| 3. We verify who you are | We will ask you to confirm your identity. This protects you — we will not hand your data to someone claiming to be you |
| 4. We acknowledge | Within 1 Business Day |
| 5. We respond | Within the period set by Act 843. We aim to respond sooner and will tell you if a request is complex and needs longer |
| 6. If we refuse | We tell you why, which right or obligation prevents us, and how to complain |
11. Marketing
Marketing
We will send you marketing only where you have agreed to receive it, or where you are an existing customer and we are telling you about services similar to those you already use.
Every marketing message contains a way to stop it, and stopping takes effect immediately at no cost to you. You can also change your preferences in the app or by contacting us.
Opting out of marketing does not stop service messages — transaction alerts, one-time codes, security warnings, statements and notices about changes to these terms. Those are part of the service and you cannot opt out of them while you hold an account.
12. Complaints
Complaints
Come to us first. Contact our Data Protection Officer at dpo@ismartpay.com.gh. We will acknowledge within one Business Day and investigate.
If you are not satisfied with our response, you have the right to complain to the Data Protection Commission of Ghana. You may do so at any time and you do not need our permission. Complaining to the Commission does not affect any other right you have, including the right to seek a remedy in court.
| Where to go | For what | How |
|---|---|---|
| Bank of Ghana | Complaints about a payment service, where iSmart Ghana has not resolved the matter within the published timeline or the outcome is disputed | Bank of Ghana, Market Conduct Office, Accra — after first raising the matter with iSmart Ghana |
| Data Protection Commission | Complaints about the handling of personal data | Data Protection Commission, Accra — after first raising the matter with the iSmart Ghana Data Protection Officer |
| Financial Intelligence Centre | Not a complaint route; the body to which iSmart Ghana reports suspicion under Act 1044 | iSmart Ghana cannot confirm or deny whether any report has been made |
| Card schemes | Disputes about a card transaction, through the cardholder’s issuing bank | Cardholders raise card disputes with their own bank, not with iSmart Ghana |
13. Changes to This Notice
Changes to This Notice
We review this notice at least annually and update it when our processing changes. Where a change materially affects how we use your data, we will tell you at least 30 days before it takes effect, by email, in the app or on our website.
The current version, with its version number and effective date, is always available on our website and in the app. We keep every published version so that the notice applying at any past date can be established.
Regulatory Basis
Regulatory Basis
| Instrument | Obligations engaged |
|---|---|
| Payment Systems and Services Act, 2019 (Act 987) | Licensing and permitted payment services; safeguarding and segregation of customer funds; transaction integrity and traceability; consumer protection and disclosure; complaint handling; incident reporting; outsourcing accountability. |
| BoG Guidelines for Payment Service Providers and Electronic Money Issuers | Wallet tiers and transaction limits; disclosure of fees and settlement terms; complaint acknowledgement and resolution timelines; treatment of dormant and unclaimed balances; agent and merchant governance; cyber and information security directives. |
| Anti-Money Laundering Act, 2020 (Act 1044) and Anti-Terrorism Act, 2008 (Act 762) | Customer due diligence before the relationship and on an ongoing basis; sanctions and politically exposed person screening; transaction monitoring; restriction and refusal of service; prohibition on disclosing that a report has been made; record retention. |
| Data Protection Act, 2012 (Act 843) | Lawful basis for every processing purpose; data minimisation and accuracy; transparency and the content of this notice; data subject rights; cross-border transfer conditions; processor obligations; security safeguards; breach notification; retention and disposal. |
| Electronic Transactions Act, 2008 (Act 772) | Validity and enforceability of electronic records, electronic signatures and click-through acceptance; retention of electronic records; electronic evidence. |
| Companies Act, 2019 (Act 992) | Corporate identity, authority to contract, and the statutory particulars stated in these documents. |
| PCI DSS v4.0.1 and ISO/IEC 27001:2022 | Protection of cardholder data; access control; encryption; logging and monitoring; incident management; supplier and processor security obligations. |
Abbreviations and Acronyms
Abbreviations and Acronyms
| Abbreviation / Acronym | Description |
|---|---|
| AML | Anti-Money Laundering |
| API | Application Programming Interface |
| BoG | Bank of Ghana |
| CDD | Customer Due Diligence |
| CFT | Combating the Financing of Terrorism |
| CX | Customer Experience |
| DPA | Data Protection Act, 2012 (Act 843) |
| DPC | Data Protection Commission |
| DPO | Data Protection Officer |
| EDD | Enhanced Due Diligence |
| EMI | Electronic Money Issuer |
| FIC | Financial Intelligence Centre |
| GhIPSS | Ghana Interbank Payment and Settlement Systems Limited |
| GhQR | Ghana Quick Response code — the national interoperable QR specification |
| GIP | GhIPSS Instant Pay |
| ISO | International Organization for Standardization |
| KYB | Know Your Business |
| KYC | Know Your Customer |
| MLRO | Money Laundering Reporting Officer |
| MMO | Mobile Money Operator |
| MoMo | Mobile Money |
| MSISDN | Mobile Station International Subscriber Directory Number |
| NOC | Network Operations Centre |
| PAN | Primary Account Number |
| PCI DSS | Payment Card Industry Data Security Standard |
| PEP | Politically Exposed Person |
| PSP | Payment Service Provider |
| PSSA | Payment Systems and Services Act, 2019 (Act 987) |
| QR | Quick Response (code) |
| RCA | Root Cause Analysis |
| SLA | Service Level Agreement |
| SOP | Standard Operating Procedure |
| STR | Suspicious Transaction Report |
| T&Cs | Terms and Conditions |
| TAT | Turnaround Time |
| TSP | Technology Service Provider |
Definitions
| Term | Description |
|---|---|
| Account | A merchant account or an end user account established on the iSmartPay platform following successful verification. |
| Acquirer | The regulated entity that maintains the merchant relationship, accepts card or wallet transactions on the merchant’s behalf and bears settlement risk. iSmart Ghana operates as a Payment Service Provider under sponsorship and settlement arrangements with its partner banks and mobile money operators. |
| Agreement | The Terms and Conditions, together with the Privacy Notice, the fee schedule, any product schedule and any order form or application accepted by iSmart Ghana, which together form the whole agreement between iSmart Ghana and the User. |
| Beneficial Owner | A natural person who ultimately owns or controls a merchant, or on whose behalf a transaction is conducted. Under the Anti-Money Laundering Act, 2020 (Act 1044) a shareholding or voting interest of 25% or more triggers beneficial ownership identification. |
| Business Day | A day other than a Saturday, Sunday or public holiday in Ghana, on which banks in Accra are open for general business. |
| Cardholder Data | The primary account number (PAN) alone or together with cardholder name, expiration date and service code, as defined by PCI DSS. |
| Chargeback | A forced reversal of a card transaction initiated by the issuing bank on behalf of a cardholder under scheme dispute rules, resulting in funds being debited from the acquirer and recovered from the merchant. |
| End User | A natural person who holds an iSmartPay wallet or otherwise uses the Services in a personal capacity. |
| Fees | The charges payable for the Services as set out in the fee schedule communicated to the User and as varied under these Terms. |
| iSmart Ghana | iSmart International Ghana Limited, a company incorporated in Ghana and licensed by the Bank of Ghana as a Payment Service Provider. |
| iSmartPay | The payment platform, applications, interfaces and services operated by iSmart Ghana under that name. |
| Merchant | A business, institution or individual accepting payments through iSmartPay under an executed Merchant Services Agreement. |
| Personal Data | Data about an individual who can be identified from that data or from that data together with other information in the possession of the data controller, as defined in section 96 of the Data Protection Act, 2012 (Act 843). |
| Reconciliation | The control process of matching iSmartPay internal transaction records against partner, scheme and bank statements to confirm completeness, accuracy and validity of value movement. |
| Refund | A merchant-initiated return of value to a payer for a transaction that was successfully authorised and captured, whether in full or in part. |
| Reserve | An amount withheld from settlement and held against actual or potential liabilities, including chargebacks, refunds and fees. |
| Reversal | The cancellation of a transaction that has not been fully completed or settled, restoring the payer and merchant to their pre-transaction financial position. |
| Services | The payment and related services made available by iSmart Ghana through iSmartPay, including collections, disbursements, wallets, scan-to-pay, invoicing and value-added services. |
| Settlement | The transfer of net funds owed to a merchant from iSmartPay settlement accounts to the merchant’s designated bank or wallet account after deduction of fees, holds and recoveries. |
| Suspicious Transaction | A transaction which, having regard to its nature, complexity, value, pattern or the circumstances of the parties, gives reasonable grounds to suspect money laundering, terrorist financing or another predicate offence, and which is reportable to the Financial Intelligence Centre. |
| Transaction | Any payment, collection, disbursement, transfer, refund, reversal or other movement of value initiated through the Services. |
| Transaction Exception | Any transaction that does not complete its expected lifecycle or that fails a control check, including stuck, orphaned, duplicated, unmatched, partially settled and mis-posted transactions. |
| User | A Merchant or an End User, and any person authorised by them to use the Services on their behalf. |
| Wallet | Stored value held for an End User on the iSmartPay platform, representing a liability of iSmart Ghana to that End User. |